Understand your service’s infrastructure without console archaeology
Your team owns services, not AWS accounts. BunBunCloud shows the slice that is yours: what it depends on, what changed, what it costs and what needs attention.
Read-only by design. No agents, no write permissions, no infrastructure changes.
What gets in your way today
Your service in a sea of resources
The account holds everyone’s infrastructure. Finding your queues, functions and databases means filtering by tags that half the resources do not have.
“What did this change break?”
A deploy, a Terraform apply or a console click changed something. Nobody remembers what it was before.
Ownership by folklore
Who owns that bucket? Who is paged when that queue backs up? The answer lives in someone’s head.
Toil that never makes the backlog
Expiring certificates, missing tags and outdated runtimes are found, then forgotten.
From the same read-only inventory
Your team’s selection, everywhere
Each team selects what is relevant to it, by account, region, service, tag or stack, and every list, graph, cost and export follows it. Switching to “All” is one click.
- Stacks group a service across environments
- Assign or release single resources
- My team page with requests to answer
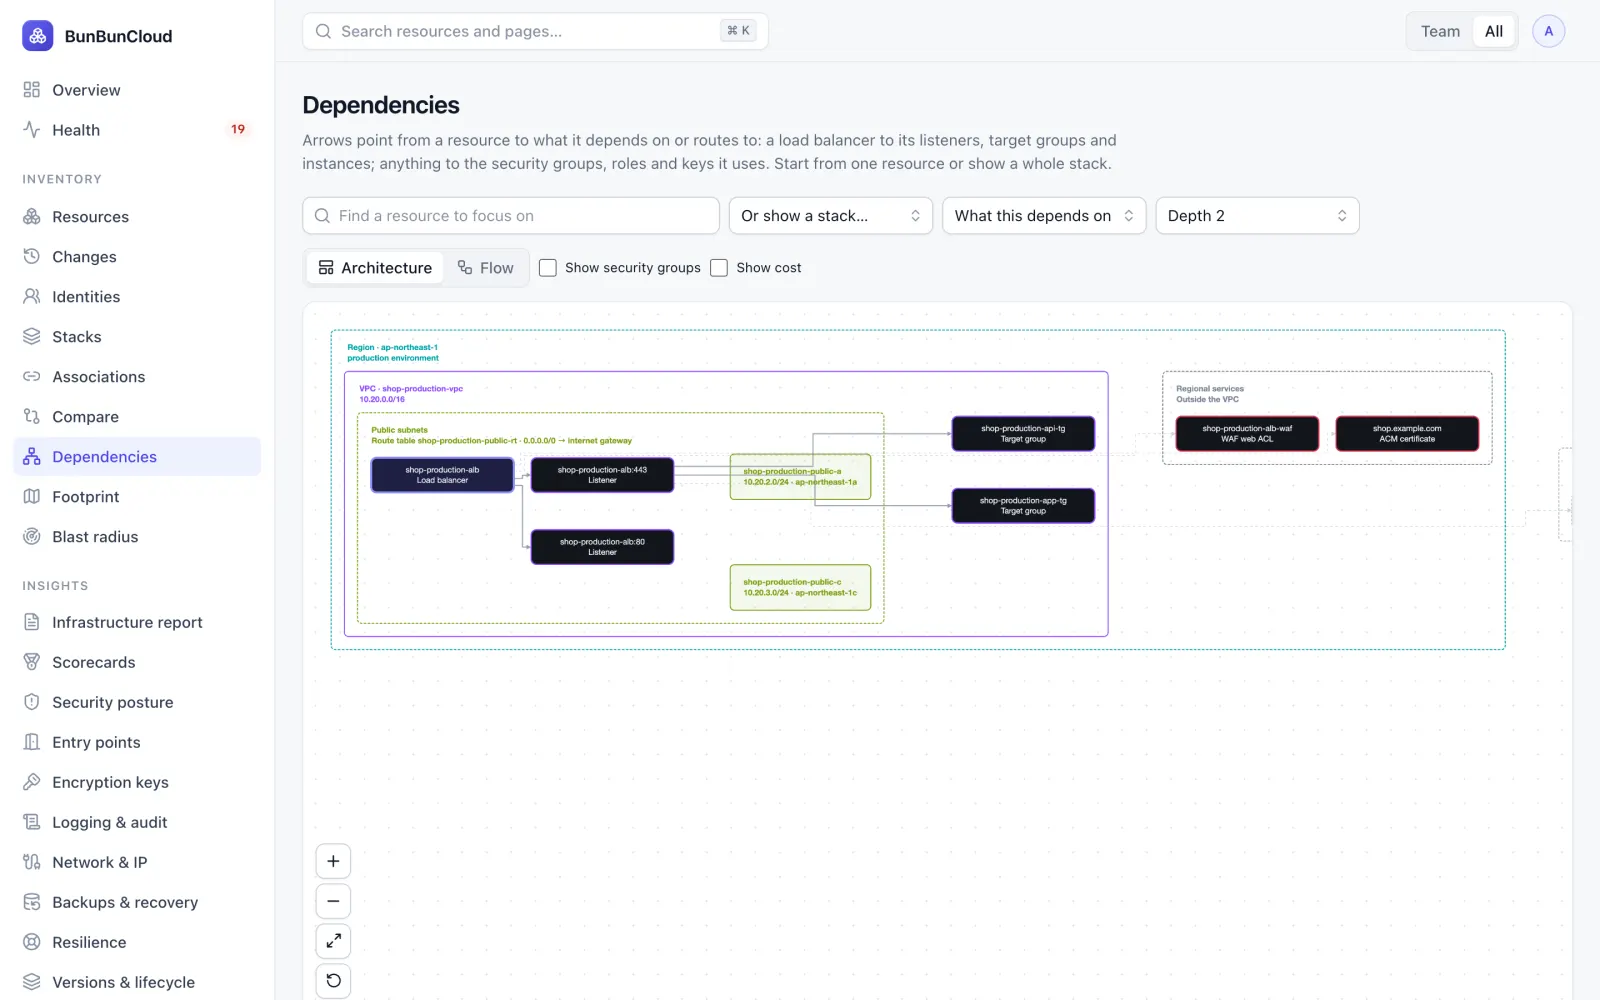
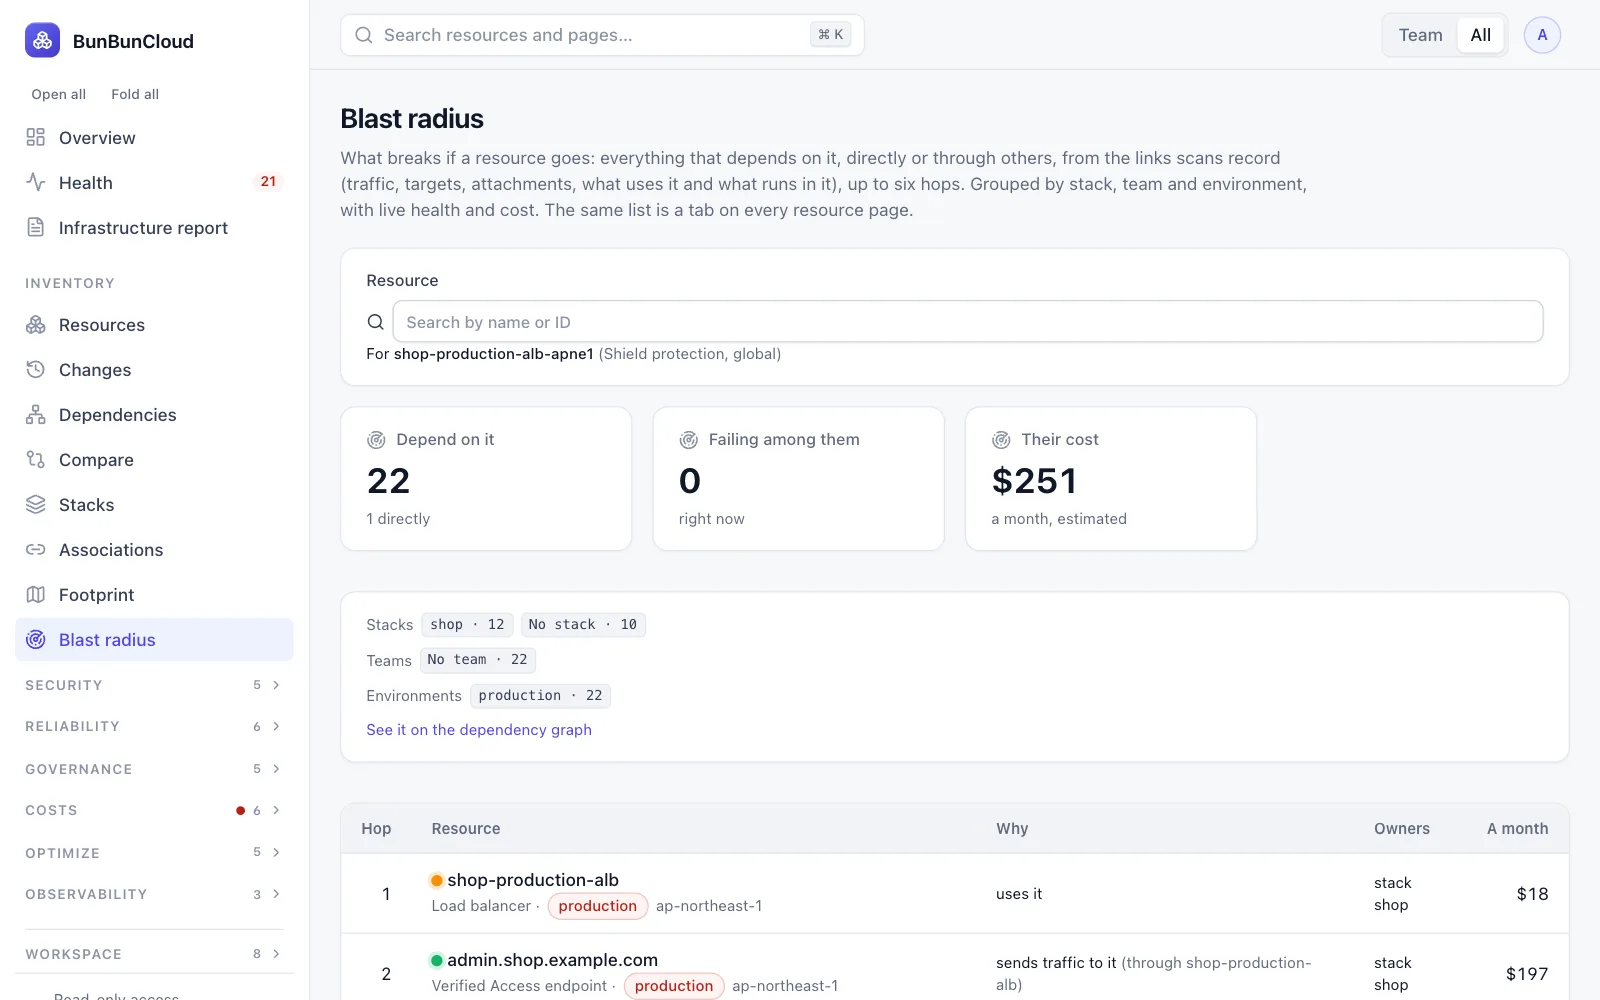
Changes and their blast radius
The changes feed lists what scans found created, changed and deleted, with the fields that changed and a diff. Blast radius shows what depends on a resource before you touch it.
- Field-by-field history per resource
- Terraform or CloudFormation that manages it
- Dependents grouped by stack and team
Findings straight into your tracker
Task automation turns findings (expiring certificates, outdated versions, missing tags, failing health) into tasks in Jira, ClickUp, Asana or Trello for the owning team, and closes them when fixed.
- Rules preview what they would create first
- One task per finding, updated and reopened
- Alerts to Slack, Teams, Google Chat and more
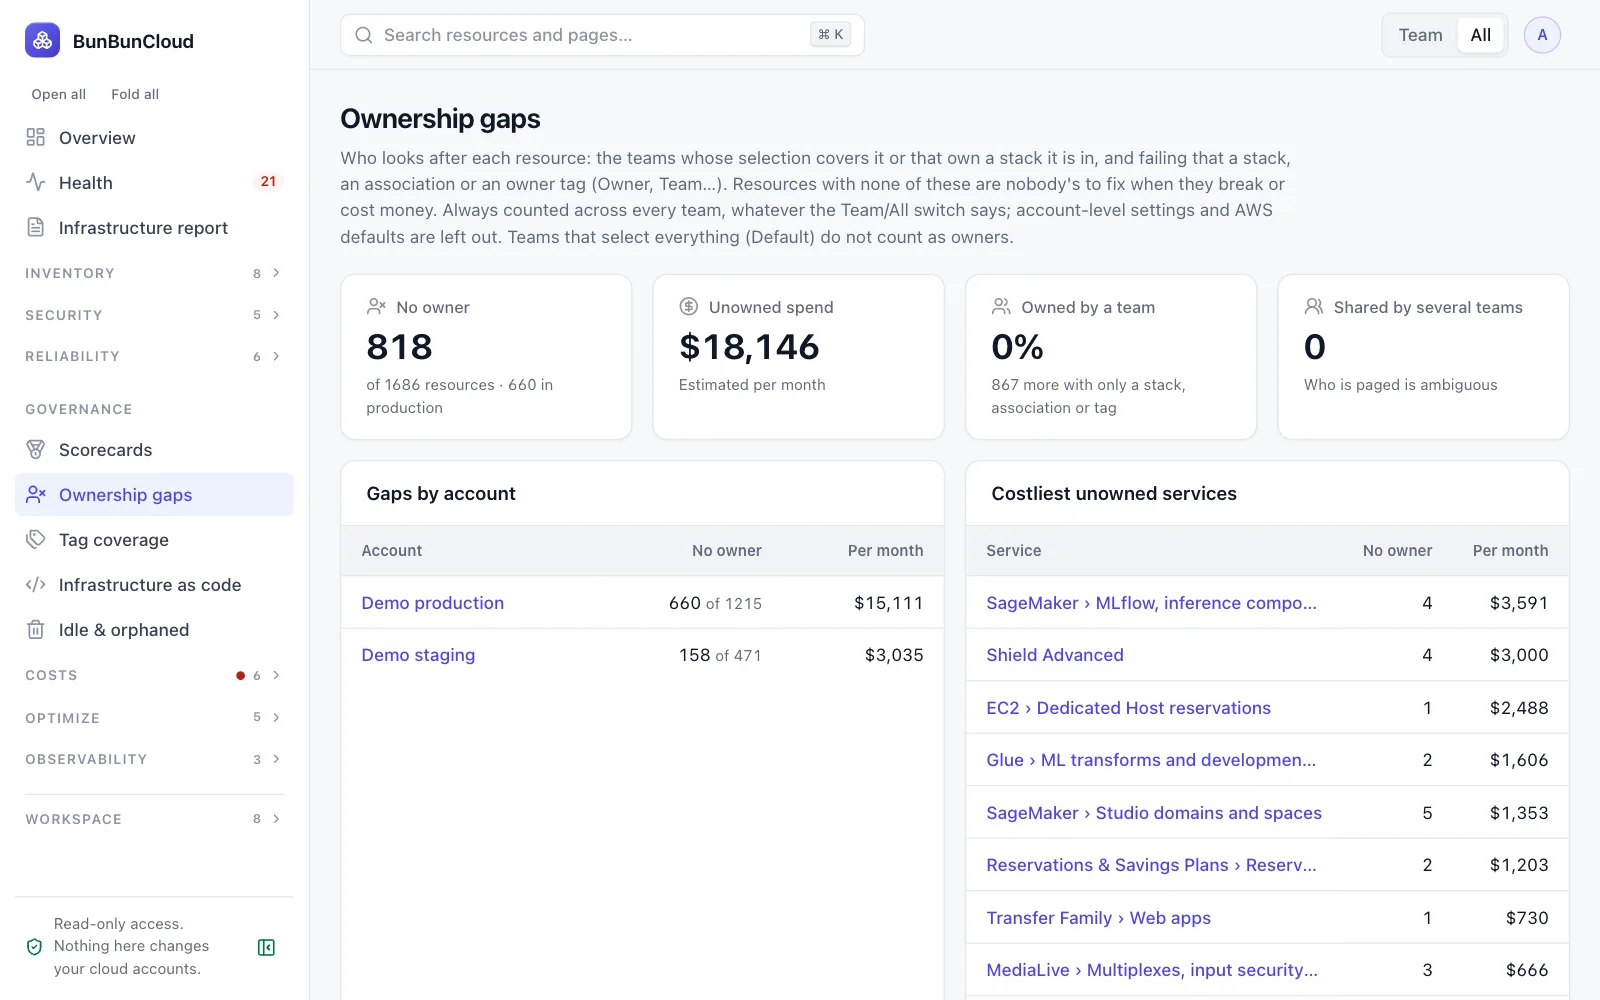
What the assessment shows you
- The dependency map of your production stacks
- What changed recently, and where
- Versions reaching end of support
- Resources nobody owns
See what you will get
The infrastructure report of our demo environment, names masked: footprint, health, drift, costs and savings.
Free, then Team
Inventory, dependencies, blast radius, changes, alerts and task automation come with Free. Team adds every insight, including ownership gaps, versions and tag coverage, and up to 10 users.
What Engineering teams ask us
Do developers need AWS console access to use it?
No. People sign in to BunBunCloud with their own account and role (viewer, editor or admin); it never hands out AWS credentials.
Does it work with Terraform?
Yes. A CI step reports what each Terraform workspace manages (addresses and IDs, never attribute values), and resources show the workspace and the last apply.
Can each team see only its part?
Each team has a selection that filters every page by default. It is a filter, not a permission boundary: people can switch to the whole inventory.
Which chat tools are supported?
Slack, Microsoft Teams, Google Chat, Discord, Lark and a signed generic webhook.
Explore by role
Know your AWS infrastructure in 10 minutes
Connect a read-only role. Get the infrastructure report: what you run, what is unhealthy, where environments differ and what it costs. Free, no commitment.