See what is exposed before someone else does
Public endpoints, open ports, unencrypted data, console users without MFA, keys pending deletion. BunBunCloud finds them in the configuration you already have, and says what to do about each.
Read-only by design. No agents, no write permissions, no infrastructure changes.
What gets in your way today
You cannot secure what you cannot see
New accounts, regions and services appear faster than any review. The inventory you audit is already out of date.
Findings without context
A list of issues is not a plan. You need to know what is behind an endpoint, who owns it, and whether it is production.
Logging gaps found during the incident
The trail that was off, the bucket without access logs, the log group kept forever: discovered too late.
Expiry dates that bite
Certificates, keys pending deletion and old access keys quietly reach their date.
From the same read-only inventory
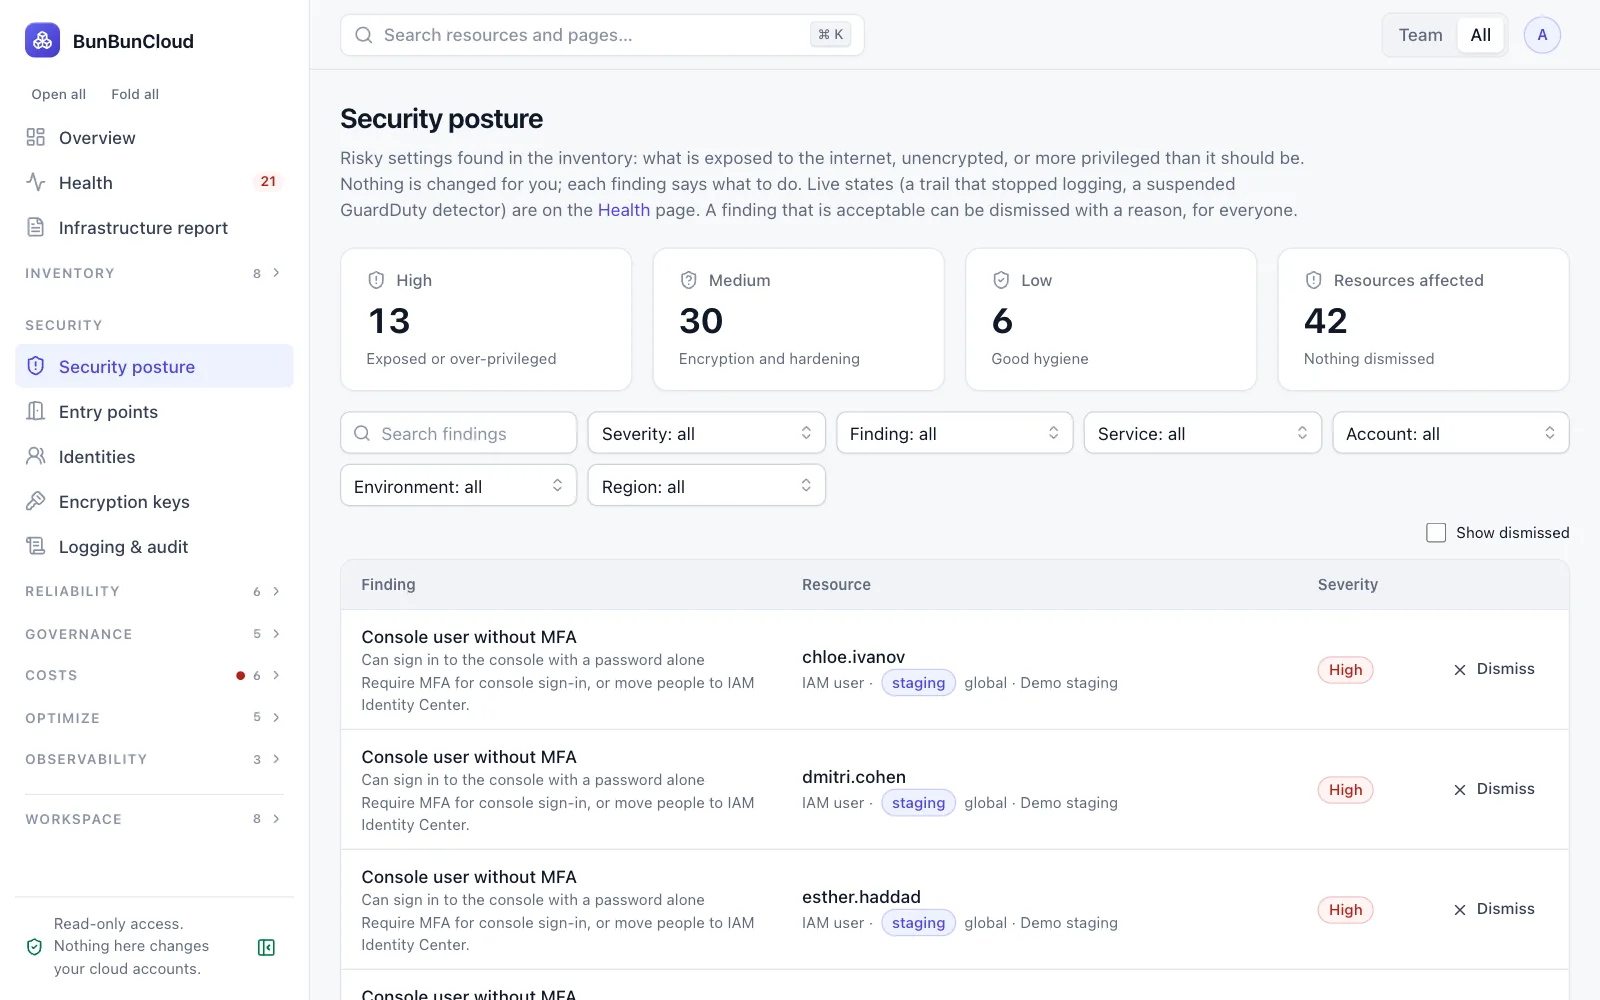
Posture findings with what to do
Public buckets and snapshots, sensitive ports open to the world, databases reachable from the internet, IMDSv1, unencrypted storage, root without MFA: each finding has a severity and advice. Accepted ones are dismissed with a reason, for everyone.
- Computed from configuration on every scan
- Severity, resource, account, region and environment
- Dismissals shared and audited
Every way in from the internet
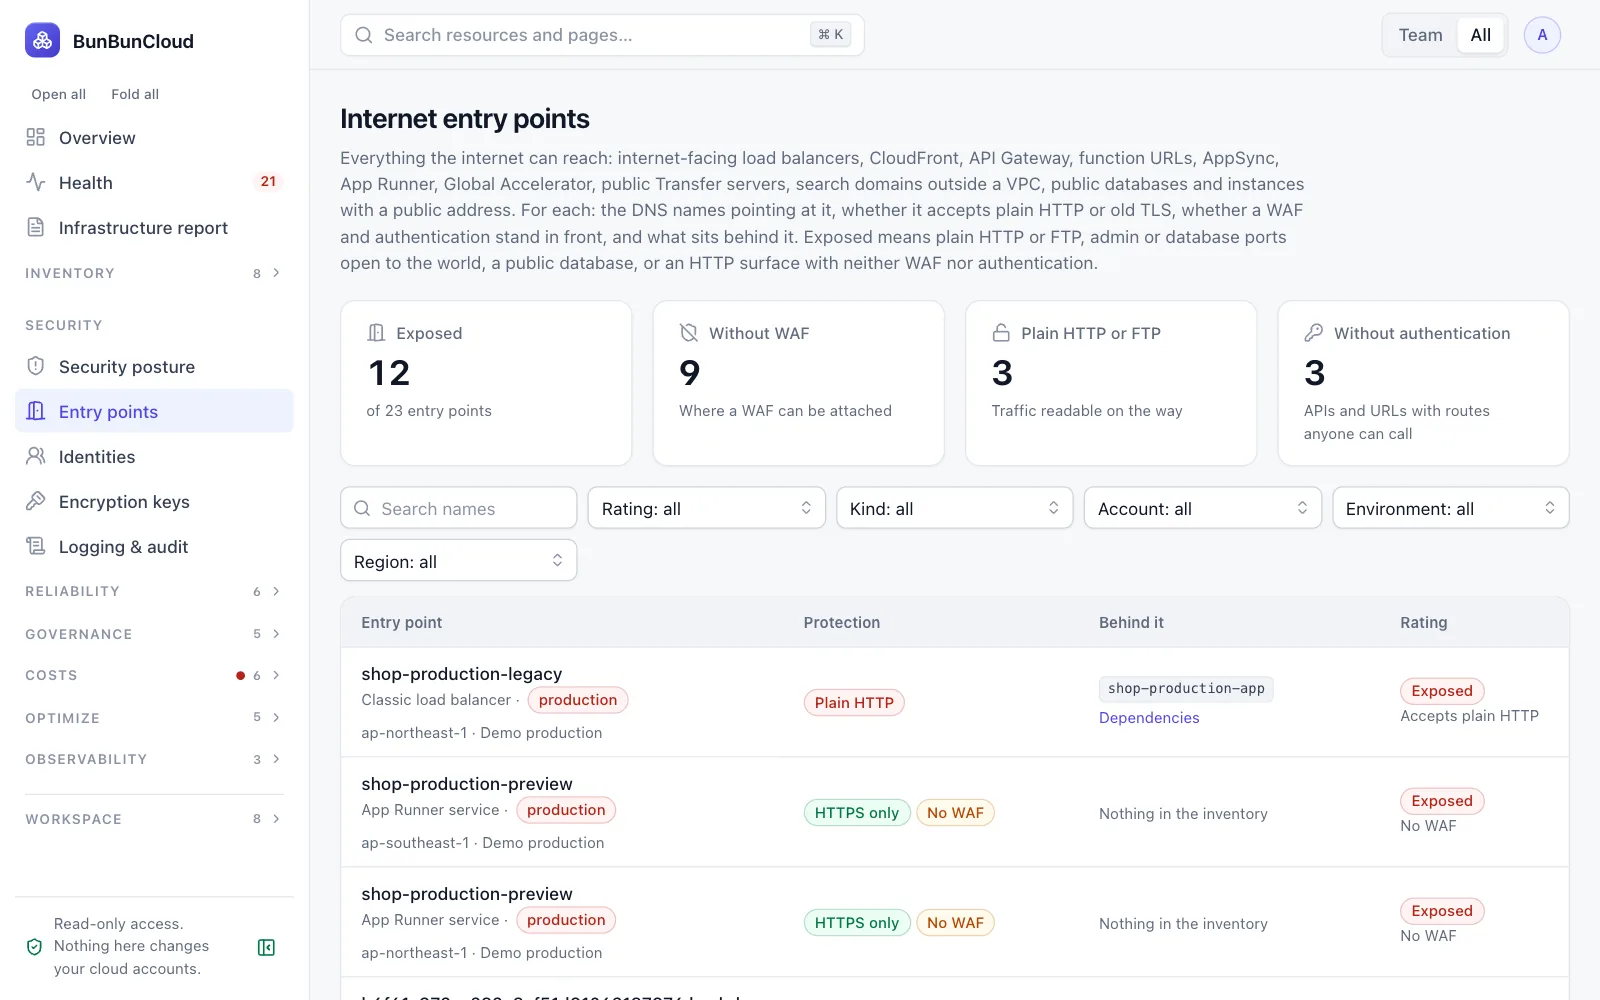
Entry points lists what the internet reaches, with the DNS records pointing at it, the transport, the TLS policy, WAF, authentication and what sits behind it.
- Exposed, partial or protected, and why
- Plain HTTP, old TLS and open sensitive ports
- Request path behind each entry
Identities, keys and logging coverage
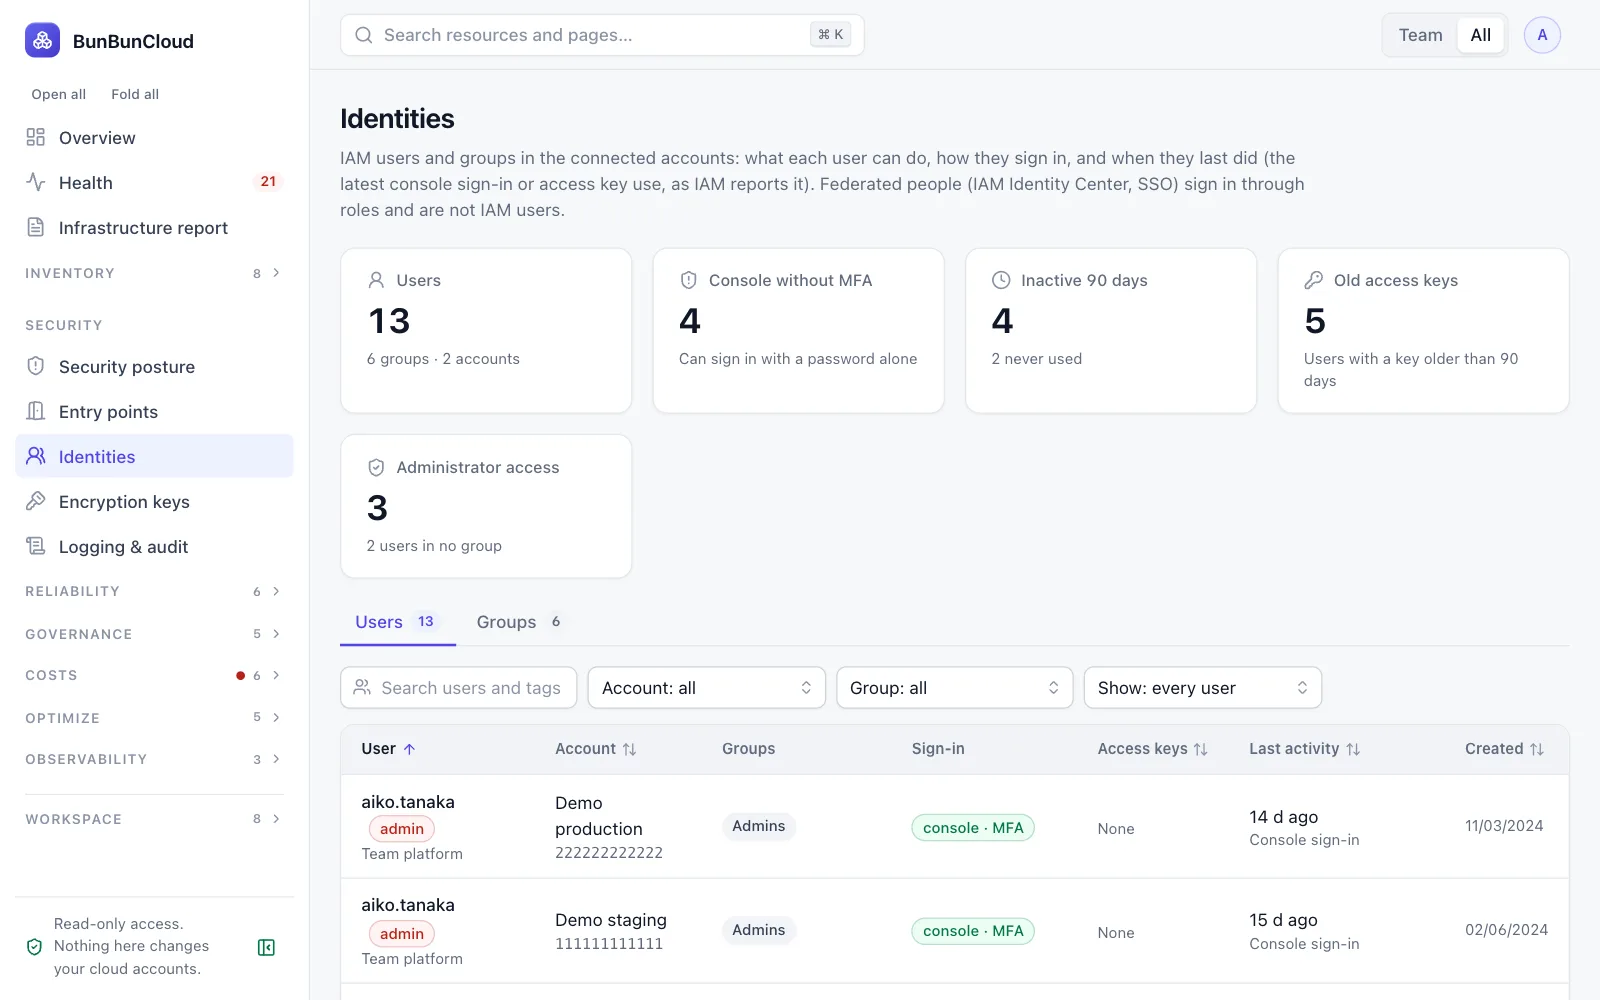
IAM users and groups with console access, MFA and key ages; KMS keys and what depends on them; CloudTrail, flow logs and access logs per account, region and resource.
- Console users without MFA, keys older than 90 days
- Keys pending deletion that something still uses
- Logging gaps, production first
What the assessment shows you
- High-severity posture findings, with the resources concerned
- Your internet entry points and how each is protected
- Logging coverage per account and region
- What expires in the next 90 days
See what you will get
The infrastructure report of our demo environment, names masked: footprint, health, drift, costs and savings.
Team
Posture and Expiring soon come with Free. Team adds entry points, encryption keys, logging, network and every other insight. Identities are on every plan.
What Security ask us
What permissions does BunBunCloud need?
A read-only role. The policy is generated from exactly the calls the collectors make, and reads no data: no object contents, secrets, messages or logs.
Do you store our secrets?
No. Secret and parameter values, messages, log events and certificate bodies are never read. Environment variable values and other sensitive fields are redacted before anything is stored.
Is this a CSPM?
It covers common posture checks from the configuration it inventories, with the context of dependencies, owners and environments. It does not claim a compliance certification.
Can findings reach our tracker?
Yes. Task automation turns findings into Jira, ClickUp, Asana or Trello tasks, routed to the owning team, and closes them when they are fixed.
Explore by role
Know your AWS infrastructure in 10 minutes
Connect a read-only role. Get the infrastructure report: what you run, what is unhealthy, where environments differ and what it costs. Free, no commitment.